Kay Consulting

supporting

Zero-Trust Infrastructure

Zero-Trust Network Architecture

Secure Every Connection, Not Just the Perimeter

Engineered advanced network isolation and micro-segmentation strategies to create security boundaries across enterprise environments. Zero-trust principles were applied to limit implicit access and ensure users, devices, applications, and workloads receive only the connectivity required for their role.
Kay Consulting

Micro-Segmentation & Access Control

Isolate Critical Systems and Reduce Attack Surfaces

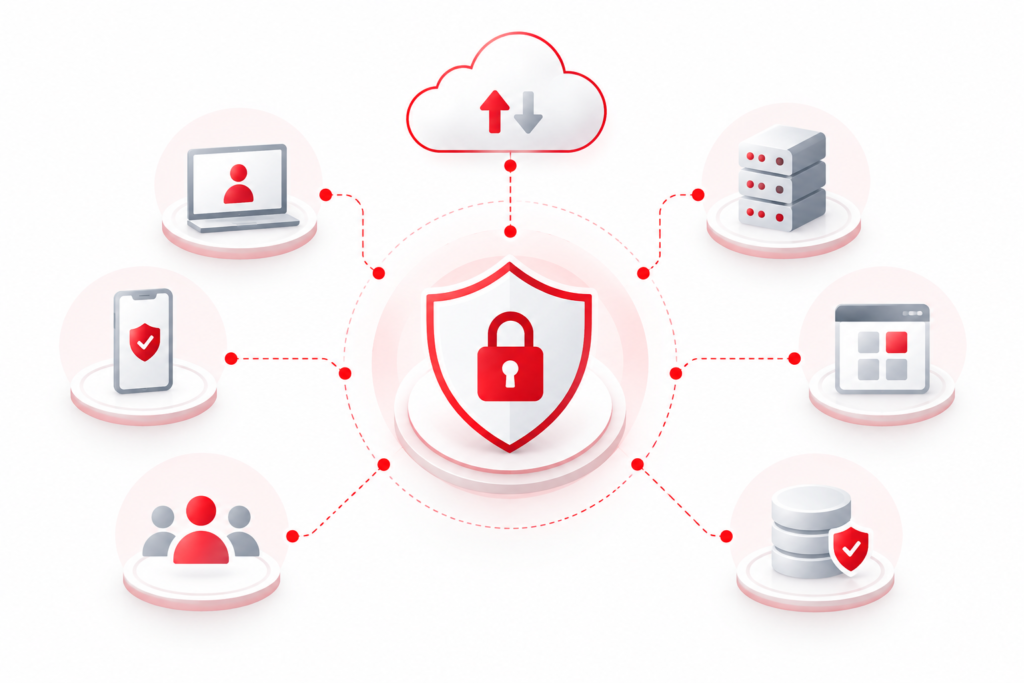
Designed segmented network environments that separate critical applications, systems, and workloads while enforcing granular access policies. This approach helps reduce unauthorized communication and limits lateral movement if an account or system is compromised.

Key Capabilities

Kay Consulting

Network micro-segmentation

Kay Consulting

Workload isolation

Kay Consulting

Identity-based access controls

Kay Consulting

Policy-driven connectivity

Kay Consulting

Lateral movement protection